Join the discussion
Write your take first — we'll ask for email only when you're ready to publish.
- Hacker News
- Single source systems provider and integrator and a doom date?
Could be a hack or a design flaw. I await the root cause analysis.
by ggm - The timing of the event at 2AM suggests something nefarious rather than an accident. That’s when it would be least likely to be noticed, but the temperatures would be high long enough to spoil all the food.
- That’s also when (poor) logic would dictate you should push a software update.by avs733
- My only question is, why would all refrigeration be under the remote control of DECA? That seems unnecessarily complicated.by HardwareLust
- This _IS_ the U.S. Government.by jpitz
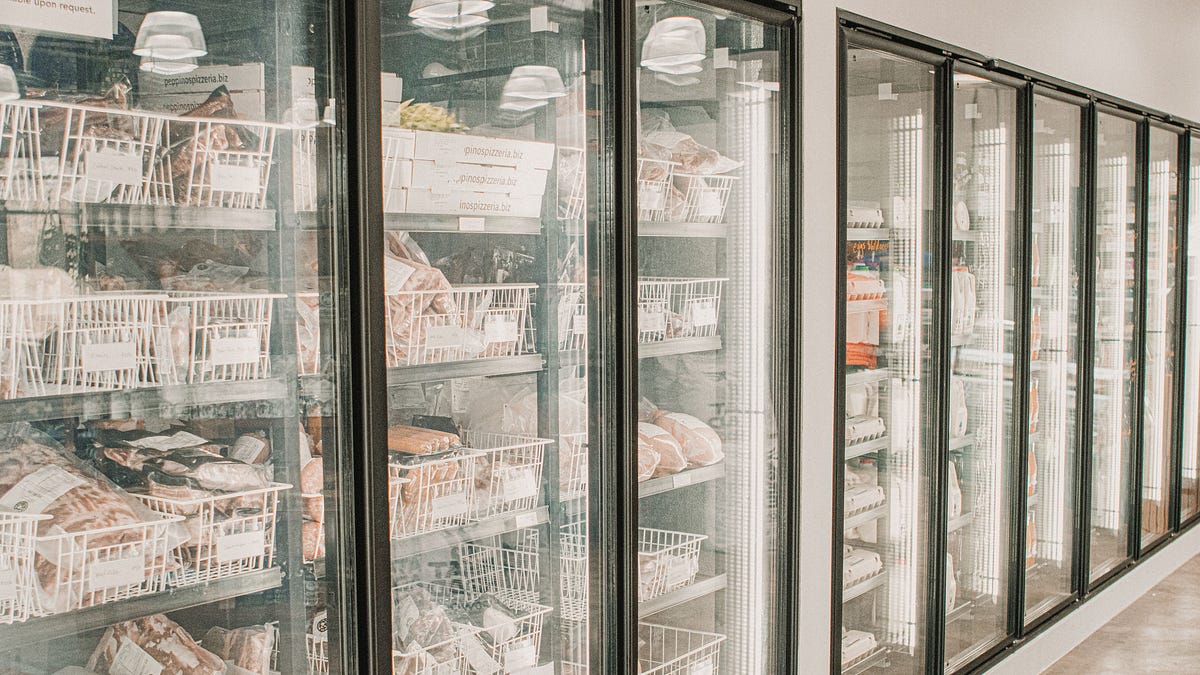
- Because they’re prefabbed walk-in coolers or freezers (at minimum, they could be purpose built cold storage warehouses) with multiple condensers, evaporators, pumps, temperature sensors, and humidity sensors. The refrigeration equipment needs some sort of control system and direct digital control is the usual way to do that these days.
This is food storage for a commissary, aka a store. They don’t use residential refrigerators.
- The article posits that they may just have centralized monitoring, not control. Since this didn't affect every location, I would assume it was a shared default password or something
- To summarize for people who TLDR: 14 freezers failed at the same time. They are all internet-controlled, and failed at the same time as a disclosure about a vulnerability. They all failed by turning on the defrost cycle and heating food.
Regardless if this was a hack or a bug, the bigger lesson is that overcomplicated systems fail in catastrophic ways. Why do military commissaries need remote-controlled freezers? It seems like a very fragile, and needless, way to run a freezer.
---
But, there are some options that the author didn't consider:
1: This could be a quickly applied patch that failed.
2: This could be a "script kiddie" hack from someone who isn't a government actor.
I'm less onboard with a state actor. Generally, when a state actor has hacked something, they don't want the victim to know. In this case, if it was a state actor, I would anticipate that they would make a single freezer fail in a way that they could verify using something like a hacked video camera or otherwise by watching public social media feeds. IMO: A state actor would only "make sense" if they knew the hole was closing soon and they don't care if they're discovered, perhaps because their operation is winding down.
by gwbas1c - These aren’t your typical refrigerator or freezer, these facilities have walk-ins or purpose built cold storage with multiple evaporators and condensing units. A building automation system is pretty standard for most buildings above a certain size, and monitoring and controlling the refrigeration is usually a part of it.
Unfortunately, I would wager that all BAS software is full of flaws and holes, allowing access to it for the public internet seems like a bad idea. I need to be on my company VPN to access our locally hosted BAS front end (which I have authorized access for) which seems like the bare minimum security.
- Iran is actively looking for ways to attack back against the United States especially against military targets without actually escalating the situation.
I'm sure some script kiddie broke into a government network, hacked an industrial process, and forced a limited supply piece of equipment into a failure mode that takes some thought and is more unique as an attack vector. It's just like buying hacks for CS source right?
by elictronic - >Generally, when a state actor has hacked something, they don't want the victim to know
Could be the Iranians, or someone aligned, conducting anti-morale operations. Could be the start of a series of small but annoying failures.
by stackghost - Could also just be a bunch of IoT devices running on synchronized time source that have what amounts to a defrost cronjob. And a latent bug that due to everything being synced and on the same schedule failed in the same manner (eg crashed the controller immediately after turning the heating element on and either didn’t boot back up or booted and some shitty programming forgot to check the heating element status). Saving state across boots or having a race condition of some sort like this gets my vote - since it’s a pretty common failure mode junior programmers are susceptible to.
I’ve seen similar too many times in my career - synchronized clocks are great until someone deploys a cronjob that fires at exactly the same time across the fleet and it breaks a certain OS or firmware revision. Which then exposes another bug that exists globally.
I definitely still subscribe to don’t attribute to malice what you can attribute to incompetence mindset.
Certainly all speculation though, real root cause will be interesting if it ever becomes public.
by phil21 - Maybe the whole point of this was not to ruin some food, but to prove infiltration of a DoD network in a way that would leak broadly because it's not classified?by mark-r
- I think it is worth mentioning that at least a couple of these bases are pretty critical from a natsec standpoint. Fort Huachuca is a big IT and secure communications installation (United States Army Network Enterprise Technology Command, the United States Army Intelligence Center, Intelligence and Electronic Warfare Directorate); F.E. Warren AFB is one of the three AFBs that operate the strategic nuclear ICBM fleet. Not saying that any classified systems were potentially hacked/at risk in this situationby thomasjudge
- Howdy y’all, author here. Just discovered this thread after wondering why Hacker News was a linked views source to my silly little freezergate braindump.
Wanted to offer a few clarifications:
I’m not a cybersecurity expert; I’m an investigator (in a totally different field), and this was essentially me following a weird thought to see where it went. My background is in natsec so that’s where my mind goes. There have since been at least dozens of additional freezer outages reported in a similar pattern, but I'm refraining from calling/tracking down every individual weirdness based on a Facebook comment at this point since there are much larger outlets with journalists more proficient than I covering this by now. Another interesting thing - There are numerous freezers and fridges within base stores, not under the control of DeCA/DoD, and none of those appear to be impacted.
I completely agree that a bad update/configuration or other shared technical failure may be the much more boring answer. The interesting part to me is that potentially hundreds of varying systems can converge upstream into common monitoring/control infrastructure. Anyone on this forum probably understands that, however IoT was something that was a relatively new concept when I was in school, and my degrees were somewhat relevant. The average person is blissfully unaware how expansive (and how much work behind safeguarding) the IoT is.
Also, since it came up: Yup. Human written. I’m pretty firmly anti-AI as a writer and also just, like, societally. I'll be sure to add some sort of footnote detailing my ai usage at the bottom of future public facing work, because I too detest reading (or questioning if what I'm reading is) slop. Minimal LLM used for understanding technical concepts and what the fuck fridge norms are…The weird formatting, excessive bolding, neurotic parentheticals, and rant energy are, unfortunately, totally my own. Sorry guys.
This was my first ever public post and intended audience was ~ 10 friends forced to read my diatribe, not thousands of strangers very validly raising questions I am not smart enough to answer myself. Appreciate the discussion and will be further educating myself on some of the points a few of you have brought up.
by meliz242 - I came to these comments coz I was curious about the AI usage here, and FWIW I also thought it smelled AI written, but I didn't think it was slop. (IMO not all AI output is slop and not all slop comes from AI).
My main question was "did Claude do the investigation by itself or just write up the article from someone's notes?"
Also though, I'm quite willing to believe this is human written and the human just happens to have a Claudey style. The actual prose isn't that Claudey it's just the structure of how it presents ideas. But, Claude had to get that structure from somewhere. It's not that surprising to see people with that style of communication.
by bjackman - Even if it isn't an attack, you demonstrated how it could be one. The vulnerability is likely there and worth mitigating. Excellent investigation and write-up!
- I thought this was excellent. It pulled together a whole bunch of interesting evidence, was very careful not to make claims that weren't supported by that evidence, and every time I had a question it answered my question in the next paragraph. Hope you publish more!by simonw
- Hi, I'm the poster. Sorry for the unexpected attention! I saw this on Bluesky and thought it was interesting enough to share here. If anything the style of your writing makes it stand out in a good way, we shouldn't always have polished/corporate-speak posts here.by jcurbo
- Impressive article. I read most of it without skimming and that is high praise from this AuDHD nerd.
It's definitely suspicious. My money is on inside job — perhaps someone not fond of the current administration's handling of things. In my experience, these types of vulnerabilities are well-known and kept in the back pocket of engineers that have a lot of experience maintaining the equipment. Everywhere I've worked has been deeply vulnerable in some way, all of the engineers knew it, and often joked about it or were counting the days to getting pwned because companies never like to spend money to address the issue. I'm sure the military is no different. Probably worse.
by jesse_dot_id - First let's acknowledge that this could very easily be a misconfiguration issue.
But, I'd be a lot more inclined to that idea if it wasn't for how they failed: they started a defrost cycle that turned the freezers into heaters, spoiling the food quicker. And the failure happened overnight, delaying discovery of the problem.
It could be just a compounding of bad luck. But an attacker with access to the specs for the freezers might be aware of how long they would stay cold after being simply shut off.
by Zigurd - I was thinking timezone update - because of course an internet-connected freezer needs updated zone info so one can configure defrost schedules without the benefit of UTC.by edelbitter
- This is eerily suggestive of a vulnerability Hank Paulson hinted at in his 2014 book "Dealing with China"
"Every nonelectric cooler comes with 25 years of free real-time monitoring. On a visit to the company in the spring of 2012, I watched as technicians in Broad Air’s space-age control room checked on the performance of its units in locations as diverse as the Adolfo Suárez Madrid–Barajas Airport in Spain; Qualcomm headquarters in San Diego, California; and Fort Stewart, the U.S. Army base in Georgia [emphasis added].
"Zhang says that 80 percent of his clients are repeaters. “If you bring long-term benefits for your clients, they will choose you.”"
by 0xWTF - America's tech-sector has a similar problem, which--until recently--was tempered by the idea that it was a dependable and predictable ally to most of its customers.
Not just in the sense of secretive kill-switches, but "US government commands you to turn over this encryption key and you're not allowed to say you did so" stuff.
by Terr_ - The author doesn't really claim it was a hack, just that it is a possibility. But they are charging down the path of the potential hack before asking the more obvious question: How many refrigerators exist in the military at all? And of those, how many are having problems?
Because a half dozen a day sounds plausible as standard maintenance issues, as the author acknowledges. If it were a hack, I'd expect something like 50% of them to have problems. But not knowing how many there are, I don't know how significant these incidents really are.
by codingdave - At the same time, I think some people in this comment section are underestimating the likelihood that this was a hack, because they're overestimating how sophisticated such a hack would have to be.
In my mind, if this was a hack, it was probably not a Stuxnet virus or something. These are smart fridges we're talking about - someone probably just logged into them using leaked credentials or a Web app vuln, and turned them off.
by wavemode - The article has a post that says this happened across 14 bases at the same time.by ckdarby
- Obvious sabotage would be addressed promptly. Subtle sabotage could persist as a minor torment indefinitely.by odyssey7
- They are charging down that path because vulnerabilities that effect the refrigerators were disclosed the same day as 14 refrigerators failed in an absurd way. They all turned on the defrost cycle and heated the food.
The problem is the author should have put a few concise bullet points at the top. (14 freezers failed at the same time. They are all internet-controlled, and failed at the same time as a disclosure about a vulnerability. They all failed by turning on the defrost cycle and heating food.)
I really recommend skimming the article to the end.
(Unfortunately, the article really is so verbose it's a borderline rant.)
by gwbas1c - A couple years ago I worked on a service that had to communicate with a Siemens S7-1500 PLC. Based on my experience with that project, none of what I’ve read recently about unsecured industrial PLCs is surprising.
I opened Siemens TIA Portal and PLCSIM for the first time and thought “wow, I didn’t think the Windows 95 GUI library was still supported.” None of the PLC contractors we had hired knew how to enable TLS on the thing (user/pass eg admin/admin was their usual). Anecdote: I once spent hours reading the docs and clicking around trying to get it to accept an SSL certificate signed by a real CA and it wouldn’t go, but it accepted one I self-signed in openssl.
In all fairness, the people who are experts in the field of Siemens PLC programming are usually mechanical-ish engineers and security is not in their skill set or on their mind.