Join the discussion
Write your take first — we'll ask for email only when you're ready to publish.
- Hacker News
- The thing with eSIMs is that they are bound to an operator, which is supposed to keep record of who is using them. Law enforcement authorities should be able to get to the guys doing this...
... unless they are tied to a government.
by harrouet - These attacks are easily done because a lot of people assume new hardware in bubble wrap is secure and wasn’t altered. There are many stories of intelligence agencies bugging the hardware after you order it, specifically online, and no, those aren’t some tinfoil hat thinking, they are actively doing it incl Europe, so always buy your device randomly from some local store and pick it up immediately, or buy it used, better yet, if you have some electronics knowledge is checking it yourself.by tamimio
- Lets start with a very basic hash. Weight of the device down to milligram. and assume if the weight does not match, its tampered with.
- how can the implant send the seed words to an attacker? doesn't a crypto wallet have to talk an application on the host computer? wouldn't the communication between the wallet and the host computer never allow for the seed words to be sent from the wallet to the outside world? in other words how could an "implant" tampering of the wallet make the host computer suddenly start sending seed phrases to third parties?by dwh452
- Shouldn't it be possible to track who bought the esim, where the data is sent, and who owns the wallets where the stolen crypto is transferred?by sorenjan
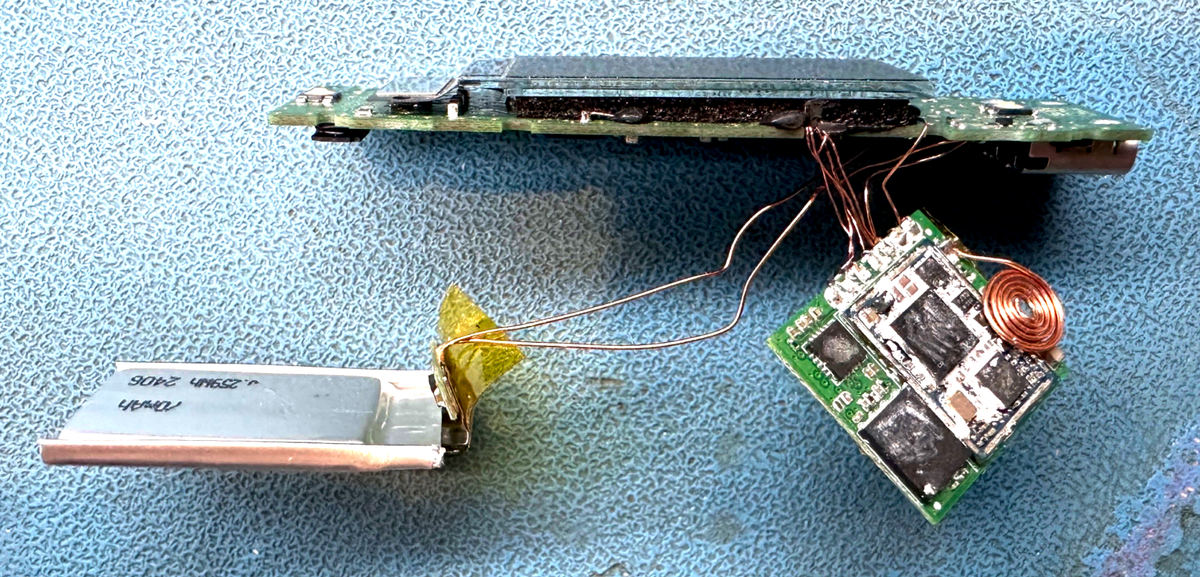
- Sad to see so many people with seemingly zero background in hardware security comfortably passing expert judgement about this attack, apparently without either looking into the security model of the attacked platform (it's public and worth a read, in my view [1]) or into the sophistication of the attack itself.
Ledger's mistake here was solely assuming that fitting hardware capable of long-range (or even global, in this case) communication into the tiny footprint of their device's case was impossible. I'm not in their industry, but I'd honestly have guessed the same until this week.
[1] https://www.ledger.com/ledger-nano-x-bluetooth-security-mode...
by lxgr - I just opened a ledger up, its stupid easy to do. Why wouldn't they make this a sealed unit with and glue it to make it impossible to open without damaging? Also why would you not glue the entire circuit board? The entire board is covered in test pads which make it super easy to solder dodgy stuff onto.by Trustable8
- Looking at the images here, there is zero attempt at security here from the ledger team. They’re using an MCU (ST MCU with Cortex M4 core) that doesn’t have any meaningful security features (ie, no secure boot, no differentiation between trusted and user mode operation - features the newer Cortex M33 core supports and newer ST parts implement). So there’s no way to guarantee that the software running on this has not been tampered with.
There is no physical tamper detection either. No tamper pads to detect case openings, no seal that gets broken when it’s opened that prevents operation. As others have mentioned, the most basic precaution would be to glue the whole thing together, which they didn’t do either.
Trusting Ledger with securing anything secret would be a very bad idea.
by acstapleton